21/09/26
Lenovo shares surged 20% in Hong Kong after the company reported record quarterly revenue of $26.9 billion. AI-related revenue increased 60% to ...
The National Assembly adopted, at second reading, amendments to the Cybersecurity Act introducing expanded European requirements for risk assessment and incident reporting. With these changes, Bulgaria transposes the provisions of the NIS 2 Directive, aimed at achieving a high level of security of network and information systems across the European Union.
Expanded scope of the law
The new legislation significantly broadens the scope of affected organizations. In addition to previously covered entities, it now includes:
The number of sectors covered by the law increases from 8 to 18, with new additions including:
New incident reporting requirements
The law introduces stricter rules for notifying cyber incidents. Organizations classified as essential and important must:
For providers of trust services, the deadline for updating information is 24 hours.
Control over technologies used
The adopted amendments also introduce mechanisms for controlling the technologies used. Upon proposal by the Cybersecurity Council, the Council of Ministers may require organizations to use:
Additionally, at the EU level, risk assessments may lead to proposals to restrict certain technologies or supply chains, particularly when originating from non-EU countries.
If a technology is restricted by a government decision, organizations must discontinue its use within three years, except in cases of high national security risk, where the deadline may be shorter.
Importance of the changes
According to the acting Minister of e-Government, the adoption of these amendments marks an important step toward strengthening Bulgaria’s national cybersecurity.
The new rules aim to improve risk management, incident response, and control over critical technologies, while aligning national legislation with European standards.
.webp)
Lenovo shares surged 20% in Hong Kong after the company reported record quarterly revenue of $26.9 billion. AI-related revenue increased 60% to ...
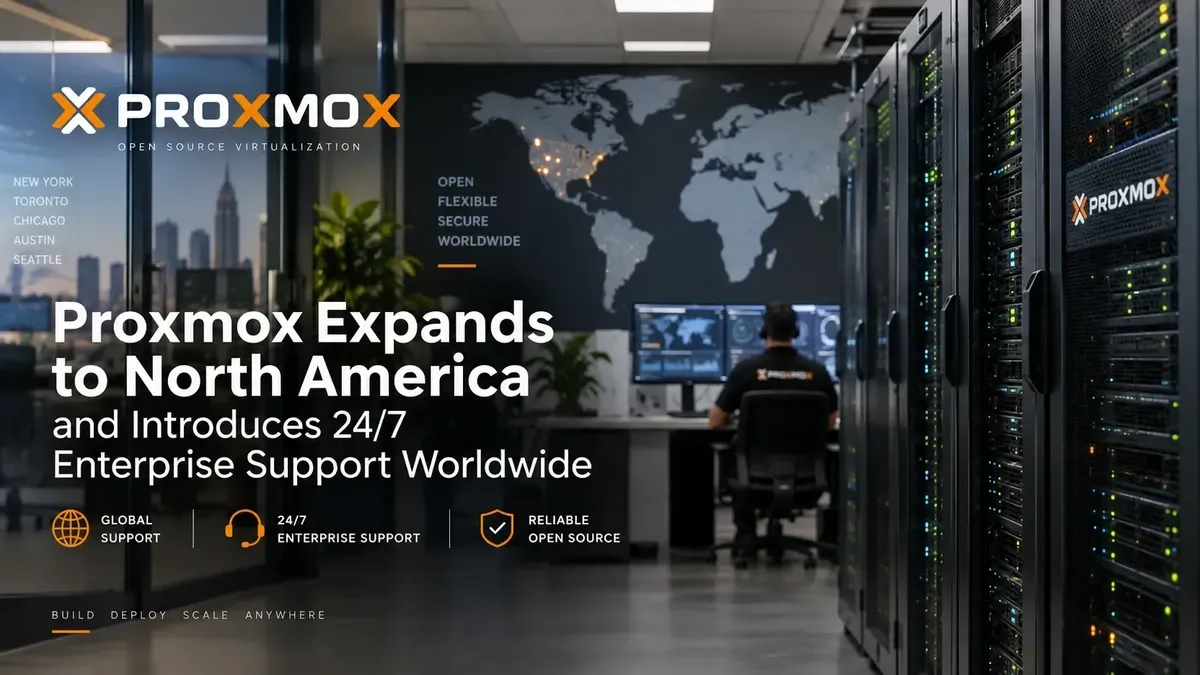
Proxmox is expanding its presence in North America with a new office in Kingston, Ontario, while introducing 24/7 enterprise support for custome...
.webp)
Oracle plans a multi-year deployment of HPE Juniper networking equipment across its AI data centers worldwide. The agreement includes routing an...
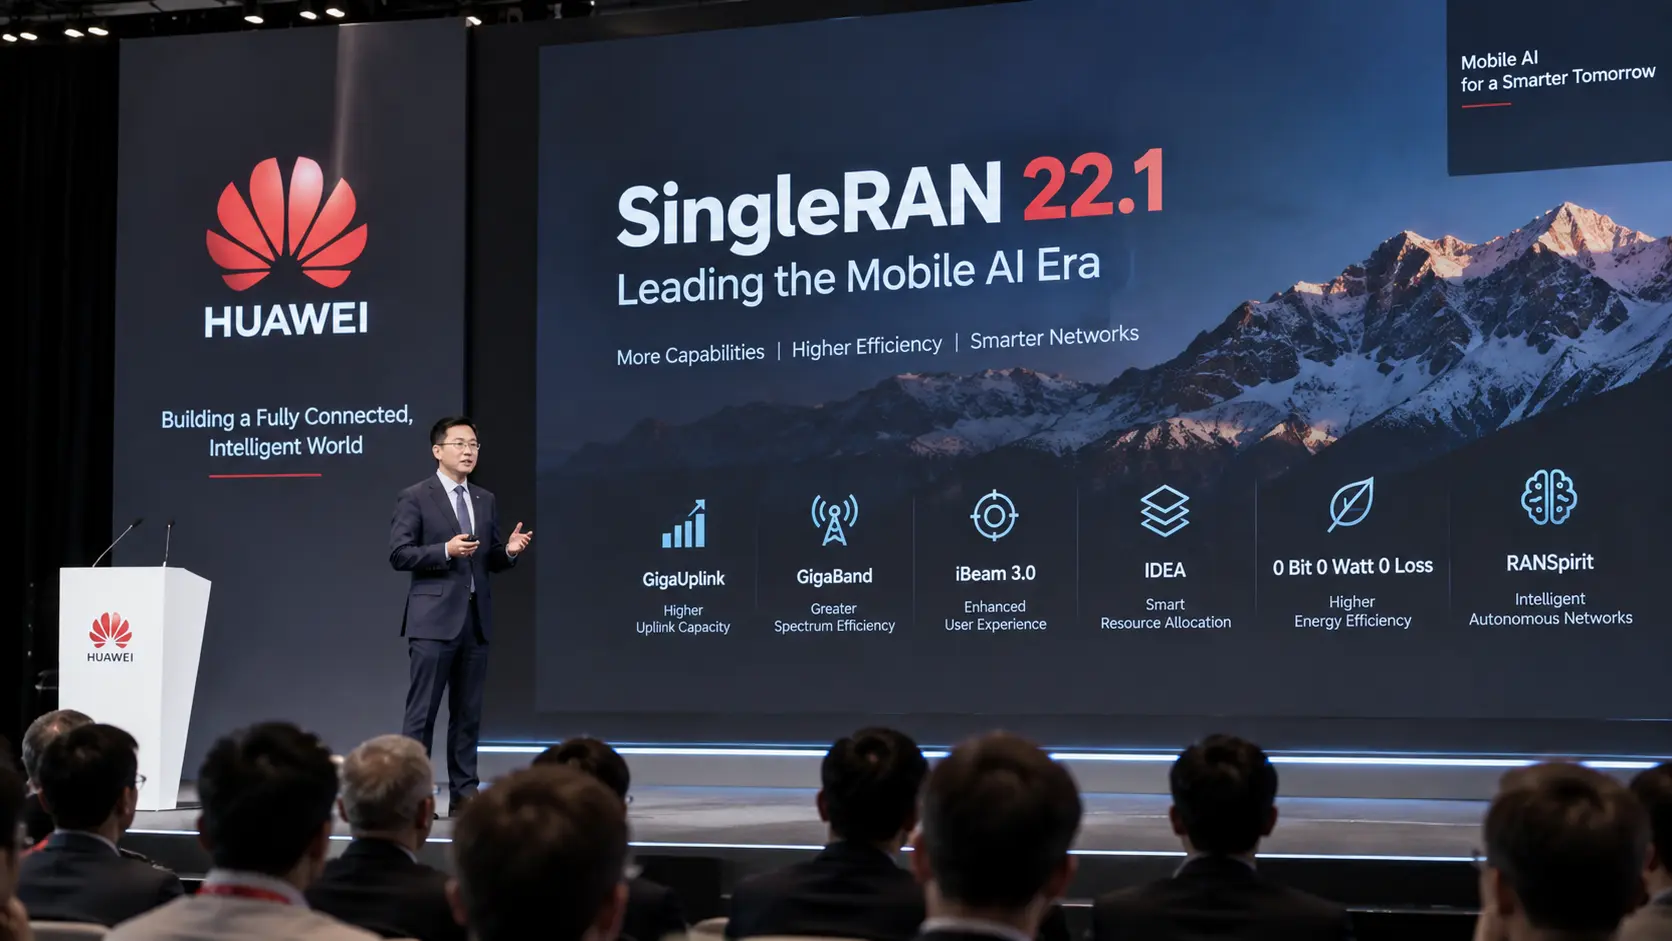
Huawei has introduced SingleRAN 22.1 as the first commercial software release designed specifically for the Mobile AI era. The new version bring...
.webp)
Lenovo is showcasing new solutions designed to improve the economics of VMware Cloud Foundation and scale AI-ready private clouds. Advanced Memo...